Twenty-five years after 9/11, the TSA recently introduced Gateside by TSA PreCheck, a program that allows eligible people without boarding passes to clear security at selected airports so they can accompany or greet friends and family at the gate. I love the idea. Before 9/11, meeting someone at the gate or seeing them off was a common ritual. The security measures implemented afterward largely eliminated it. Whether those measures were appropriate at the time isn’t my point. What’s interesting is what happened afterward. A system designed to prevent something extraordinarily consequential also eliminated something valuable that was much harder to measure.
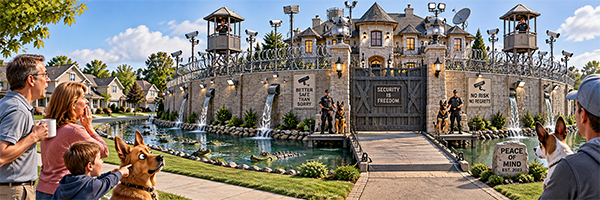
Organizations face this problem all the time. Every organization needs some form of Defense. Legal controls protect against litigation and regulatory exposure. Financial controls protect against fraud and insolvency. Cybersecurity protects information and technology. Safety protocols protect people. Policies, approval authorities, and other controls protect organizations from countless undesirable outcomes. The problem is that Defense can become excessive. In fact, the people responsible for Defense often have perfectly rational reasons for wanting more of it. Legal professionals don’t want the company sued. Finance professionals don’t want it to become insolvent. Cybersecurity professionals don’t want a breach. Within each of those domains, additional protection can look entirely reasonable. But a Defense mechanism can be locally optimal within the risk domain it protects while being globally suboptimal for the organization.
Every additional control can have countervailing effects elsewhere. More approvals may reduce financial exposure while slowing decisions. More restrictive security policies may reduce cyber risk while making collaboration more difficult. Additional legal controls may reduce liability while constraining how employees interact with customers. Measures intended to protect an organization can eventually interfere with the very activities, relationships, and behaviors the organization depends upon to succeed. An organization can become so well defended that it can no longer do what it was designed to do.
This becomes especially dangerous after something goes wrong. When an organization experiences a lawsuit, fraud, breach, accident, or other significant undesirable event, the natural reaction is to prevent it from ever happening again. The event provides empirical evidence that the risk is real, but it does not necessarily prove that the organization’s Defense was inadequate. No reasonable system eliminates every risk. Even appropriately designed Defense leaves some residual risk. Occasionally, that risk will materialize. If every undesirable event is interpreted as evidence that Defense was inadequate, protection can become accretive. An event occurs, another control is added, another event eventually occurs, another control is added, and Defense becomes progressively more restrictive.
The problem is compounded by what leaders can measure. A lawsuit is visible. A security breach is visible. A financial loss is visible. An accident is visible. The ingenuity that disappeared because employees lost autonomy is harder to see. So is the trust eroded by excessive controls, the Organizational Tension those controls may create, the customer interaction that never happened, or the opportunity lost because a decision took too long. What Defense prevents is often easier to see than what excessive Defense takes away.
That’s why Defense cannot be designed in isolation. It is one element of Organizational Design and must remain aligned with the rest of the organization. When leaders add a control, they should evaluate not only the risk it mitigates, but also how that control affects the organization’s people, processes, authority, Culture, and ability to execute its strategy. This doesn’t mean organizations should become cavalier about risk. Effective Defense requires leaders to understand which risks should be prevented, which should be mitigated, and which must simply be accepted as part of operating the organization. The objective of Organizational Defense is not to eliminate risk. It is to manage risk without unnecessarily compromising the organization it exists to protect.
Executive Insight:Measures designed to protect an organization can make it less effective when their impact on the rest of the Organizational Design is overlooked.